Blog

Insights, guides, and product updates

10 posts tagged with "splunk"

View All Tags

Announcing Alert Manager Enterprise 4.0 at Splunk .conf26

Datapunctum8 min read
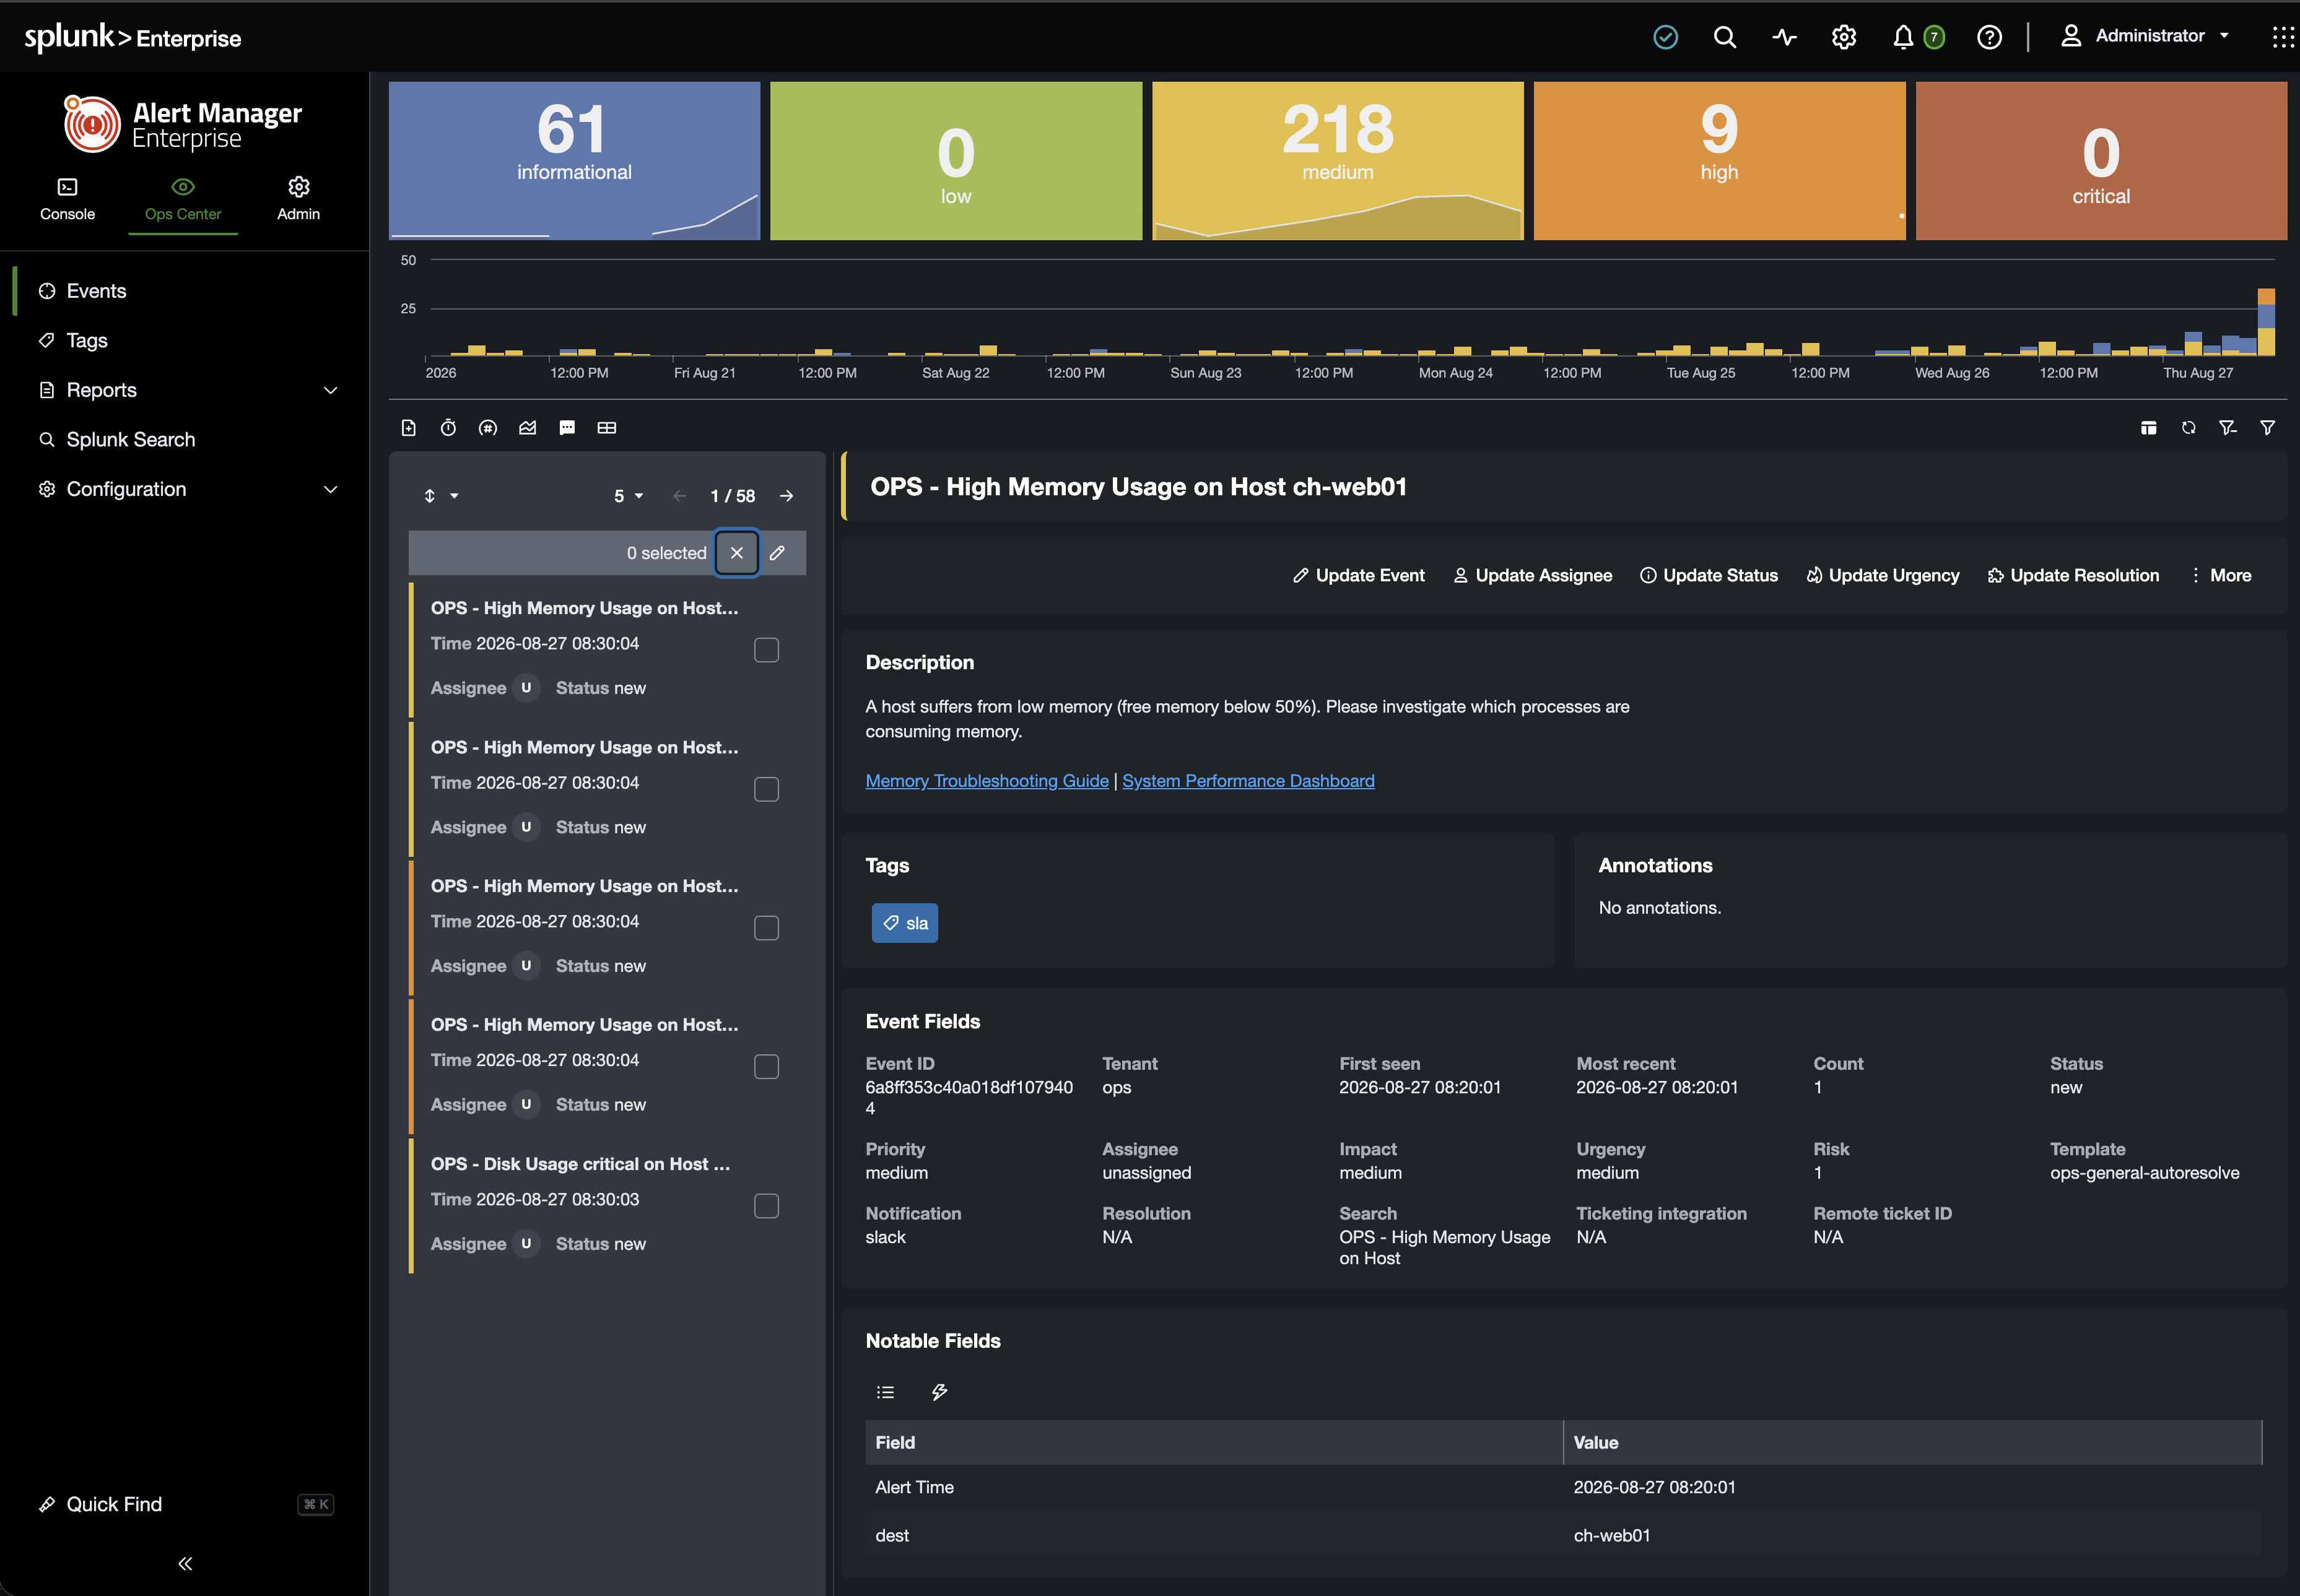
Alert Manager Enterprise 4.0

We’re excited to introduce Alert Manager Enterprise 4.0, with a redesigned interface that makes investigating alerts and managing configuration easier. For teams using Vulnerability Intelligence, a new PostgreSQL backend provides the foundation for managing larger vulnerability datasets.

Get a first look at Splunk .conf26 in Denver, September 14–17, 2026, with a live preview at the Datapunctum booth. General availability is planned for Q4 2026. Join us to explore the new experience and discuss what it means for your team.
AME Release: 3.9

Datapunctum2 min read

Alert Manager Enterprise 3.9.0

AME 3.9.0 focuses on making event investigation faster, adding more context directly inside AME, improving observable mapping workflows, and tightening reliability across ticketing, vulnerability ingestion, and event handling.

AME for Electric Utilities

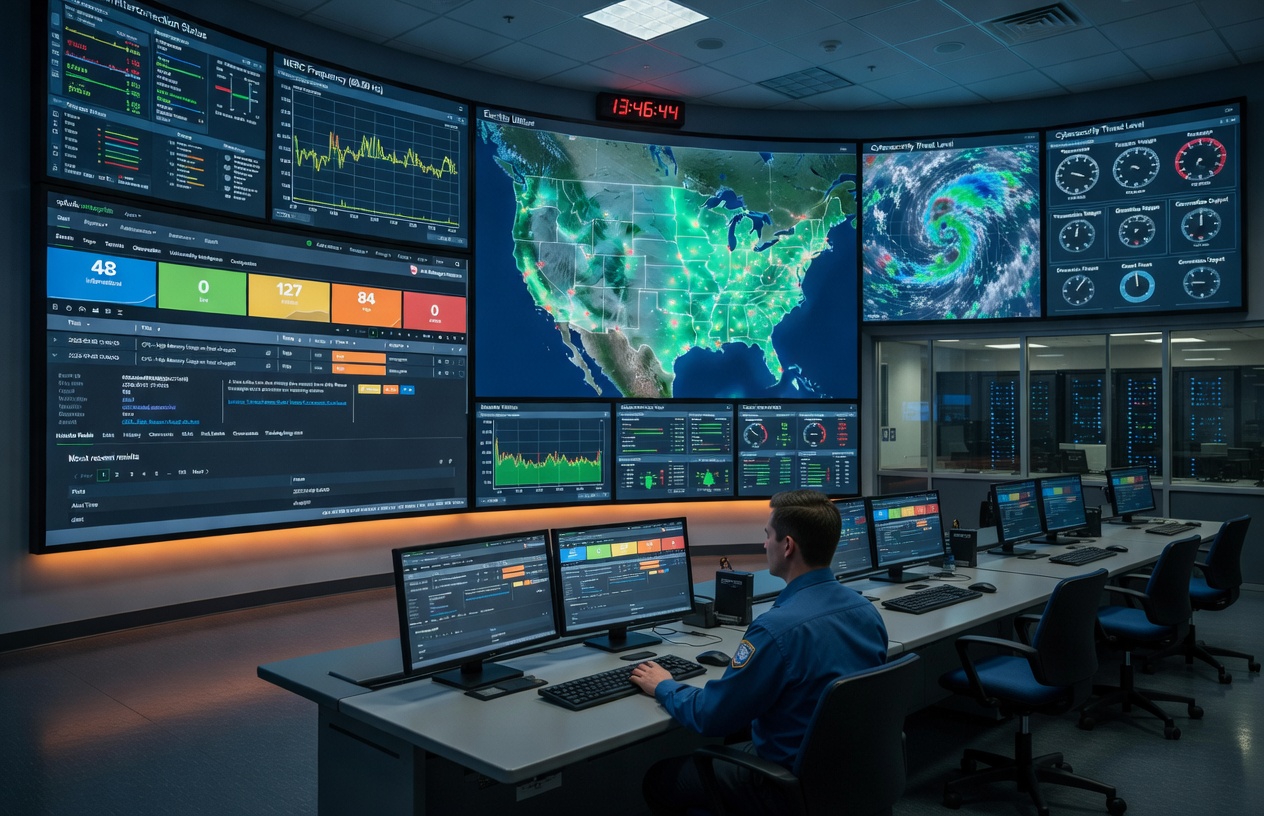
Electric utilities face some of the world's strictest cybersecurity mandates. NERC CIP standards require continuous monitoring, rigorous access controls, fully auditable incident handling, and strict separation of critical assets - all without ever moving sensitive data outside your secure perimeter.

Alert Manager Enterprise (AME) helps grid operators meet these requirements with a structured, auditable alert lifecycle that stays entirely inside their existing Splunk environment.

If you already use Splunk for visibility and alerting, AME turns your current Splunk alerts into compliant workflows - without external tools, data egress, or heavy custom development.

No new consoles. No compliance gaps. Just reliable event management that supports grid protection and simplifies audits.

AME Release: 3.8

Datapunctum2 min read

Alert Manager Enterprise 3.8.0

This release brings targeted improvements for quicker manual workflows, more customizable notifications, expanded vulnerability data sources (including native Microsoft Defender support), enhanced deployment flexibility, and stronger remediation tracking within Vulnerability Intelligence

Everything You Need to Know About SSL for Splunk in 2022

Datapunctum15 min read

Everything You Need to Know About SSL for Splunk in 2022

This blog post provides the definitive answer to all questions regarding SSL usage in the Splunk Enterprise product suite. The blog describes every possible SSL configuration in the Splunk configurations and helpful tips and tricks. With the release of Splunk 9.0 on June 14, 2022, new configuration options were introduced. The configuration that only applies to Splunk versions after 9.0 are prefixed with an according prefix.

A huge thank you goes to Duane Waddle & George Starcher for their .conf 2015 talk Best Practices for Splunk SSL (TheSSLippery Slope Revisited) that served as a reference book for all things SSL for many years.